This guide contains everything you need to know about conducting an information security risk assessment questionnaire at your organization.
Isora GRC gives security teams one connected workspace to operationalize third-party risk management, with vendor questionnaires for HECVAT, SIG, and CAIQ, a connected vendor inventory covering deployments, contracts, and data classifications, risk tracking and documented exceptions, and scorecards and reporting that prove compliance to auditors and procurement, all in one place.


Managing third-party risk is challenging when questionnaires go out by email, responses come back in different formats, and SOC 2 reports sit in a forgotten folder. As the vendor population grows, renewal reviews slip, exceptions expire, and no one can produce a defensible answer when an auditor asks who has access to PII.
Distribute prebuilt HECVAT questionnaires alongside custom questionnaires for SIG, CAIQ, and other vendor formats. Several contributors can work on one questionnaire at once, so vendors collaborate on responses, upload evidence alongside each question, and route submissions for internal approval through an interface built for the people who take assessments. Meanwhile, completion tracking covers the entire vendor population in real time.
Keep one record per vendor with its full history, covering assessment results, product deployments across organizational units, data classifications, contacts, contracts, risk ratings, and exception documentation. Search and filter by service type, data sensitivity, risk level, or organizational unit to answer auditor questions against current data.
Publish assessment findings to the risk register with lineage back to the question that identified the gap, the vendor and product it affects, and the data at stake. Assign owners, set remediation deadlines, and document exceptions with expiration dates while the append-only audit log records every action. In Isora, vendor findings and internal findings all live in the same register.
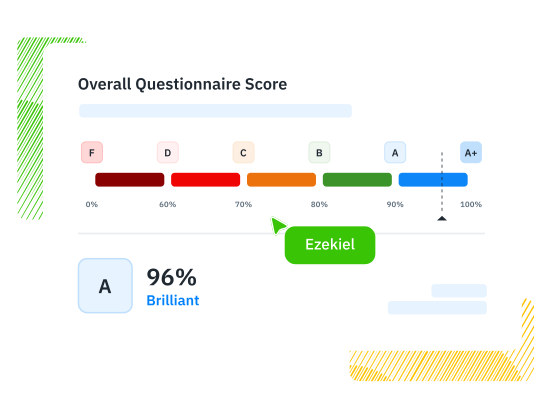
Generate reports and scorecards from questionnaire completion rates, control gaps, and risk ratings by vendor, product, or organizational unit, and export them for procurement committees, governance boards, and audit reviews. Keep approval and rejection decisions consistent and documented with standardized scoring across every reviewer.
Third-Party Risk Management Software: Tools, Platforms & How to Choose Third-party risk management (TPRM) software is the system a security...
Third-Party Risk Management Frameworks: How to Build and Govern a TPRM Program A third-party risk management (TPRM) framework is the structure an...
Vendor Risk Assessment: How to Evaluate Third-Party Risk A vendor risk assessment is the process of evaluating the security, financial, operational,...
Supplier Risk Management: How to Assess, Tier, and Monitor Supplier Risk Supplier risk management is how security teams identify, score, and monitor...
TPRM Maturity Model: How to Score Third-Party Risk A TPRM maturity model is a self-assessment framework to score how developed a third-party risk...
HECVAT vs VPAT: What’s the Difference and When Do You Need Each? HECVAT and VPAT evaluate different aspects of higher education procurement...
Vendor risk management software helps security teams assess, track, and manage risks from third-party vendors. Isora GRC connects vendor questionnaires, inventory records, and risk data in one workspace, so questionnaire responses, evidence, and findings stay traceable to the vendor they describe.
Vendor monitoring platforms provide external security ratings and risk signals as one input, while Isora GRC manages the full vendor assessment lifecycle. It covers questionnaire distribution, response collection, evidence management, risk tracking, and reporting. Still, the two can work together, with monitoring signals feeding the program that Isora runs end to end.
Yes, Isora GRC can handle HECVAT vendor assessments. In Isora, the one-click HECVAT uploader imports completed spreadsheets, matches responses, and scores automatically. It also supports custom questionnaires for SIG, CAIQ, and other vendor assessment frameworks, plus HECVAT Full and HECVAT Lite distribution directly through the platform.
In Isora GRC, vendor assessment findings flow directly into the same risk register used for internal assessments. Every vendor risk carries lineage back to the questionnaire, the specific vendor and product, and the data classification at stake. That way, vendor risk stays part of the organization’s unified risk picture.
Yes, Isora is designed for vendor populations from 20 to 500+. Standardized scoring, real-time completion tracking, and the one-click HECVAT uploader are specifically built for the throughput that growing vendor programs demand. Higher education institutions managing hundreds of vendors use Isora as their primary vendor assessment platform.
Isora includes dedicated support for HECVAT (with the one-click uploader for Full and Lite versions) and prebuilt questionnaires for common compliance frameworks. For SIG, CAIQ, and other vendor-specific frameworks, teams can build custom questionnaires with conditional logic, weighted scoring, and approval routing.
Isora deploys in weeks with no-code setup, minimal IT lift, and no outside consultants. Teams can send a first vendor questionnaire without months of configuration, and adding internal assessments later reuses the same inventory and risk register.